Model Legislative Text: Giving Congress Standing Access to Program Data
POPVOX Foundation is releasing draft legislative text that would give Congressional committees, GAO, CBO, and CRS direct, standing, automated access to the data federal agencies collect when they run programs. We wrote it as a modular section: drafters can drop it into an authorization bill or an annual appropriations measure and name the program it covers, either by statutory citation or by funding heading and fiscal year. See legislative text below.
Why we wrote it
Last week, nearly every conversation our team joined in DC came back to data.
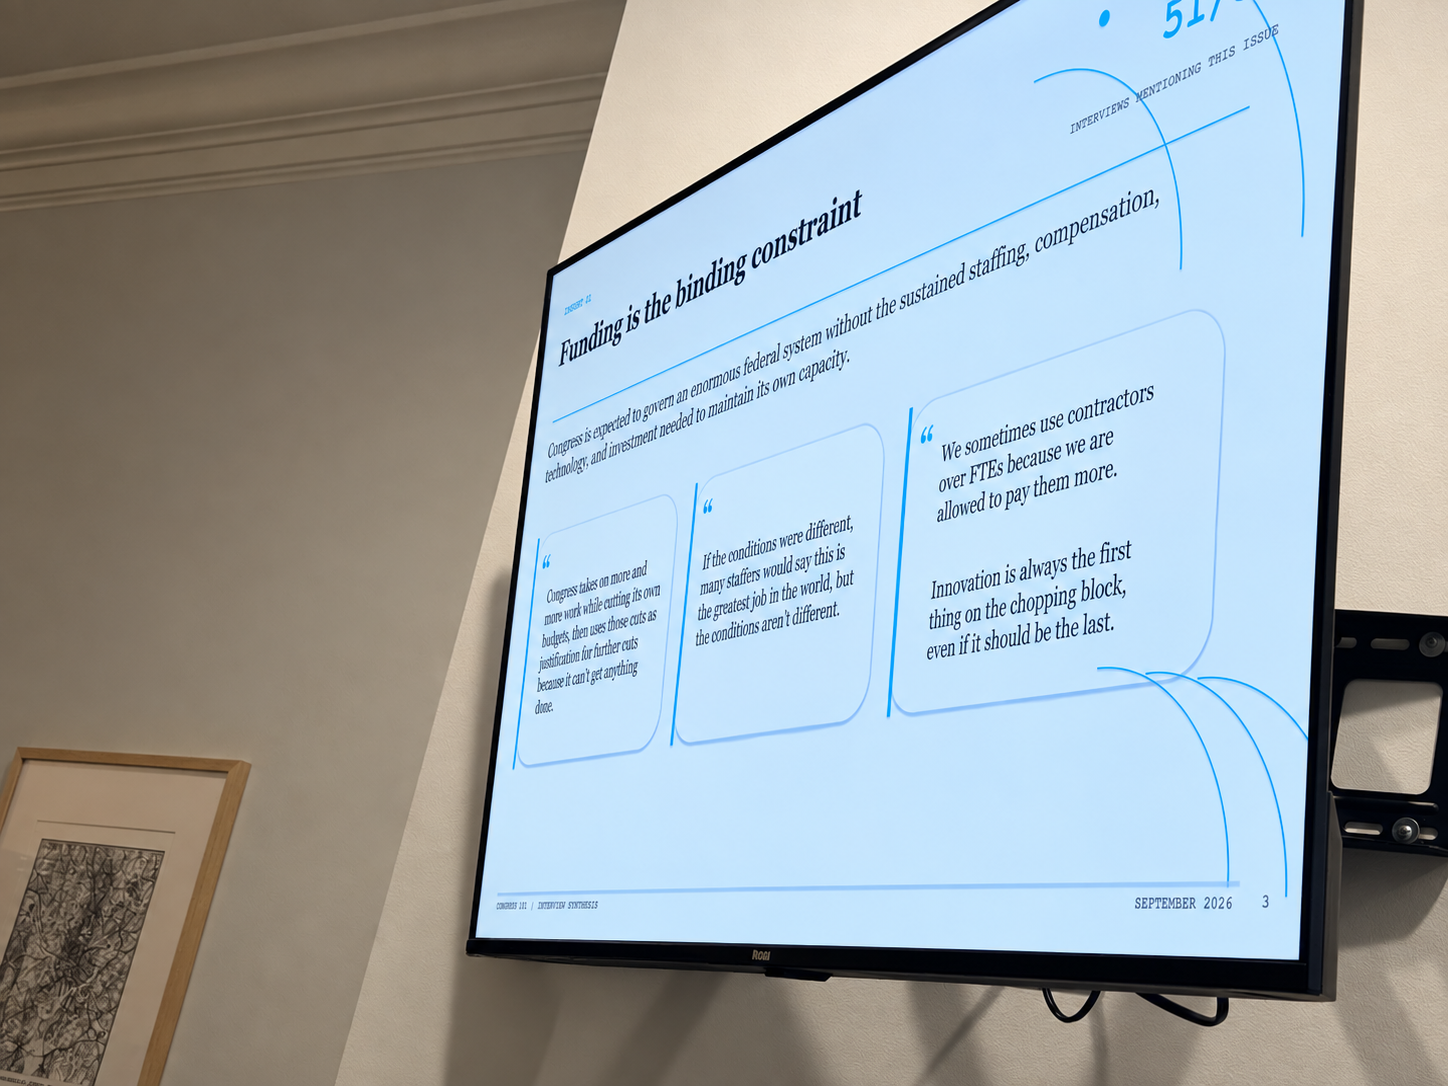
On Tuesday, POPVOX Foundation Executive Director Marci Harris and Managing Director Aubrey Wilson met in person with representatives from a major tech company to discuss the infrastructure and incentives behind public data access, and how AI can make legislative data more transparent and resilient. That evening, Senior Manager of Government Innovation Ashley Nagel led the public launch of the Three Horizons for Congress Project (H3). H3 builds on a decade of Congressional modernization work by organizing more than 200 reform ideas on a three-horizon timeline that separates the practical from the theoretical. Over a quarter of those ideas address how Congress gets and uses data.
On Wednesday, Marci spoke at a Senate Homeland Security and Governmental Affairs Committee roundtable on the relationship between the Executive and Legislative branches, alongside representatives from the American Enterprise Institute, American Governance Institute, Bipartisan Policy Center, Georgetown University, and Niskanen Center, as well as Acting Comptroller General Orice Williams Brown. Panelists kept returning to data and Members’ and staffers’ needs to find and use it on short notice. Data is the report card to show Congress whether programs deliver the outcomes Congress intended. As the House and Senate adopt modern technologies, AI tools that support them perform only as well as the data they have access to. When it comes to the support agencies the Legislative branch relies on, the Acting Comptroller General told the room that GAO lacks the Executive branch data it needs to carry out its auditing and accountability work more effectively.

On Wednesday and Thursday, Aubrey joined a Data Foundation working group on a new National Data Strategy. Participants from across the Executive branch and major public policy data organizations shaped the discussion, and Aubrey described what Congressional data access looks like in practice: offices rarely have access to large program datasets, often don't know those datasets exist, and seldom use them in policymaking or oversight. Program implementers also have few ways to tell legislators what they see on the ground.
Offices rarely have access to large program datasets, often don't know those datasets exist, and seldom use them in policymaking or oversight. Program implementers also have few ways to tell legislators what they see on the ground.
These conversations pointed to a problem Congress can fix in statute.
Today, a committee that wants program data usually has to ask for it, wait, and accept whatever the agency sends back, often a summary or a dashboard. Our draft legislative text replaces that request-and-wait process with a standing right of access.
Who gets access
The text covers every House and Senate committee and subcommittee with legislative, appropriations, or oversight jurisdiction over the program, plus GAO, CBO, and CRS. A committee's chair and ranking member can each designate staff and technical experts and use the access independently, without the other's sign-off. CRS does not need a committee to authorize its access.
What they get
Agencies must share the data they create, collect, or receive in running the program, including what contractors and grantees report to them, along with metadata, data dictionaries, corrections, and prior versions. Congress gets data at least as complete and current as what agency staff and contractors use to run and evaluate the program. A dashboard or agency-written analysis does not satisfy the requirement. Agencies must keep historical data for a set retention period and log every correction, deletion, and revision with its date and reason. They cannot silently change or remove data they have already shared.
How they get it
Agencies must provide machine-readable data in documented, nonproprietary formats through secure electronic systems that support automated discovery, querying, bulk retrieval, and updates. The text defines automated access to include software acting on behalf of an authorized user, which covers the AI tools Congressional offices increasingly rely on. Recipients may retrieve, retain, and analyze the data with tools they choose. The text doesn't mandate a particular protocol or product (such as APIs) because although there are ideal technology solutions at this time, they may not be the most ideal in the future. The text also does not require Congress to build its own repository. Every two years, agencies must consult Congressional recipients on whether the access works and fix what doesn't.
No throttling, no gatekeeping
Agencies may not rate-limit, cap, or otherwise throttle authorized access, and they must maintain enough system capacity to handle it. Congressional recipients don't have to seek case-by-case approval, file a request for each use, sign agreements federal law doesn't require, or explain what they plan to look into. Agencies may keep access logs only for authentication, security, and system operation, and may not use those logs to identify or disclose what Congress is investigating.
Protecting sensitive information
Agencies apply safeguards that match the sensitivity of the data, but they cannot use those safeguards to block authorized access. For identifiable data, an agency may offer a secure analysis environment, as long as recipients can still run their own automated analysis. Congressional recipients must protect nonpublic data under applicable law and chamber rules, and access alone doesn't authorize public release.
Grants and contracts
For programs that run through grants, contracts, or cooperative agreements, new, renewed, and materially amended awards must require recipients to submit the data they already report in machine-readable form, with enough documentation to interpret it. The provision adds no new reporting categories.
When access breaks down
If access goes down, data arrive late, or an agency claims a statute bars it from sharing particular data with a particular recipient, the agency head must notify affected recipients within one business day, with separate notice to a committee's chair and ranking member. The notice must name the affected data, the cause or specific statutory basis, what remains available, and when the agency expects to resolve the problem. Agencies may suspend access only to contain an active cybersecurity incident or imminent compromise, and only for as long as strictly necessary. Heavy use and inadequate system capacity don't qualify.
Accountability
Each year, agency heads certify to Congressional recipients whether they complied, and report on data timeliness, system availability, interruptions, withheld data, and corrective actions. An agency that certifies noncompliance must submit a corrective action plan within 30 days and keep Congress updated until it fixes the problem. GAO may review compliance and report to the committees of jurisdiction. The text also preserves every existing authority Congress and its support agencies hold to obtain information.
Fork it and Implement it
Bracketed items in the draft legislative text, including implementation deadlines, update intervals, and retention periods, leave room for committees and legislative counsel to fit the provision to a specific program.
Do you have feedback on how to improve the draft legislative text? We want to hear from you. Email us at marci@popvox.org.
Legislative Text
SEC. __. CONTINUING CONGRESSIONAL ACCESS TO PROGRAM DATA.
(a) DEFINITIONS.—In this section:
(1) COVERED PROGRAM.—The term “covered program” means [identify the program by name and statutory citation or, for an annual appropriations measure, by the applicable funding heading and fiscal year].
(2) COVERED AGENCY.—The term “covered agency” means each Federal agency that administers the covered program.
(3) COVERED PROGRAM DATA.—The term “covered program data” means data created, collected, received, or maintained by or on behalf of a covered agency in administering the covered program, including data required by law or agreement to be reported to the agency by a contractor, grantee, subgrantee, or other program participant. The term includes underlying records, associated metadata and data dictionaries, corrections, and prior versions. Where geographic identifiers are collected for the program, those identifiers shall be included at the level of detail available, subject to applicable disclosure law.
(4) COVERED CONGRESSIONAL RECIPIENT.—The term “covered congressional recipient” means—
(A) each committee or subcommittee of the House of Representatives or the Senate having legislative, appropriations, or oversight jurisdiction over the covered program, as determined under the rules of the respective House;
(B) the Comptroller General of the United States;
(C) the Director of the Congressional Budget Office; and
(D) the Director of the Congressional Research Service.
(5) AUTOMATED ACCESS.—The term “automated access” means access by software, including software acting on behalf of an authorized user, to discover, query, retrieve, or receive updates to data without manual action by covered agency personnel for each use.
(6) OTHER TERMS.—The terms “machine-readable” and “metadata” have the meanings given those terms in section 3502 of title 44, United States Code.
(b) STANDING ACCESS.—Each covered agency shall provide each covered congressional recipient direct, standing, and secure access to covered program data for the performance of the recipient’s official duties. A recipient may designate personnel to exercise that access, including committee staff and technical experts consistent with the rules of the respective House. The chair and ranking minority member of a committee or subcommittee may each independently designate personnel and exercise equivalent access under this section, without approval by the other. Access by the Congressional Research Service under this section shall not require separate authorization by a committee. Subject to subsection (f), access includes the ability to retrieve, retain, and analyze covered program data using tools chosen by the recipient.
(c) MEANS, CURRENCY, AND INTEGRITY.—
(1) Not later than [implementation deadline], each covered agency shall make covered program data available through secure electronic means supporting automated discovery, querying, bulk retrieval, and receipt of updates. The data shall be machine-readable and provided in documented, nonproprietary, interoperable formats. No particular technical protocol or product is required.
(2) The data available under this section shall be no less complete than the data available to covered agency personnel or contractors for administration or evaluation of the covered program, except to the extent disclosure to a particular recipient is prohibited by a Federal statute.
(3) At least once every [2] years, each covered agency shall consult covered congressional recipients about the usability of the means of access and shall make updates needed to maintain the capabilities required by this subsection.
(4) Each covered agency shall provide the definitions and documentation needed to understand the source, meaning, completeness, quality, update schedule, and revisions of covered program data.
(5) New covered program data and corrections shall be available not later than than the earlier of—
(A) the time they become available to covered agency personnel or contractors for administration or evaluation of the covered program; or
(B) [update interval] after the covered agency creates, receives, or records them.
(6) Each covered agency shall maintain access to historical covered program data for at least [retention period] and shall preserve a record of corrections, deletions, and revisions, including their dates and reasons. The agency may not silently replace or remove data previously made available under this section.
(7) A dashboard, summary report, or agency-produced analysis does not substitute for access to the covered underlying data. This subsection does not require a separate legislative branch repository.
(d) UNLIMITED ACCESS; NO GATEKEEPING.—Access under this section shall be unlimited as to the frequency, volume, and duration of authorized queries, retrievals, and updates. Neither a covered agency nor a person acting on its behalf may impose rate limits, query quotas, volume caps, or other measures that throttle authorized access. The covered agency shall maintain capacity sufficient to support such access. A covered congressional recipient shall not be required to obtain case-by-case approval, submit a separate request for each use, enter into an agreement not required by Federal law, or disclose a proposed line of inquiry as a condition of access.
(e) CONFIDENTIALITY OF CONGRESSIONAL USE.—A covered agency may collect and retain only the access records reasonably necessary for authentication, system security, and operation. Neither the agency nor a person acting on its behalf may use those records to identify, infer, or disclose a covered congressional recipient’s substantive lines of inquiry. Access to those records shall be limited to personnel responsible for system security and operation, except as required by law.
(f) PROTECTION OF INFORMATION.—Each covered agency shall apply authentication and safeguards appropriate to the sensitivity of covered program data without using those safeguards to restrict access authorized by this section. Where identifiable data require additional protection, the agency may use a secure analysis environment or comparable method that preserves the recipient’s ability to conduct independent automated analysis. A covered congressional recipient shall protect nonpublic data in accordance with applicable law and, in the case of a committee or subcommittee, the rules of the respective House. Receipt under this section does not authorize public disclosure. A claim that a Federal statute prohibits disclosure to a particular recipient shall be handled under subsection (i).
(g) REPORTING THROUGH AWARDS.—To the extent the covered program is carried out through contracts, grants, cooperative agreements, or similar awards, each covered agency shall include in awards entered into, renewed, or materially amended after [date] terms requiring data already required to be reported under the award to be submitted in machine-readable form, with accompanying documentation sufficient to interpret the data. This subsection does not itself require collection of new categories of data.
(h) EXISTING AUTHORITIES.—Nothing in this section limits any other authority of a committee, the Comptroller General, the Congressional Budget Office, or the Congressional Research Service to obtain information, or authorizes withholding of information otherwise available to such recipient.
(i) INTERRUPTIONS AND WITHHELD DATA.—
(1) If access is materially interrupted, covered program data are not made available when required, or a covered agency contends that a Federal statute prohibits disclosure of particular data to a covered congressional recipient, the head of the agency shall notify each affected recipient not later than [one business day] after becoming aware of the circumstance. Notice to an affected committee or subcommittee shall be provided separately to its chair and ranking minority member.
(2) The notice shall identify the affected data; the cause of the interruption or the specific statutory basis for withholding; the portions that remain available; the steps being taken to provide or restore access; and the expected resolution date. The agency shall promptly provide all portions that can be disclosed and, during an interruption, an alternative means of access to the extent feasible.
(3) A covered agency may temporarily suspend access only to the extent and for the time strictly necessary to contain a documented, active cybersecurity incident or imminent material compromise of system security. It shall give notice as soon as practicable and restore access promptly. Ordinary authorized use or inadequate system capacity is not grounds for suspension or throttling.
(j) ACCOUNTABILITY.—
(1) Not later than [date] and annually thereafter, the head of each covered agency shall certify to each covered congressional recipient whether the agency has complied with this section. The certification shall describe data timeliness and system availability, material interruptions, data withheld, and corrective actions taken during the preceding year.
(2) If the agency certifies noncompliance, its head shall submit a corrective action plan to the covered congressional recipients not later than [30] days after the certification and provide updates until the noncompliance is corrected.
(3) The Comptroller General may review compliance with this section and report findings and recommendations to the committees described in subsection (a)(4)(A).